Implementing and Operating Cisco Security Core Technologies
Read questions, check verified answers and discuss the reasoning. Use reading options to shape your revision, or switch to the simulator for timed practice.
50 questions in this view
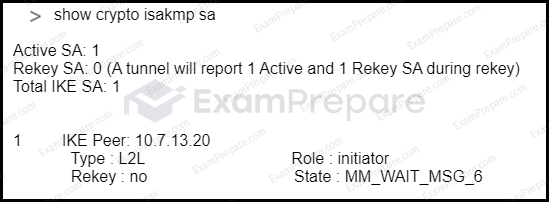
Refer to the exhibit. During the rollout of a new site-to-site VPN between a headquarters Cisco Secure Firewall Threat Defense and a partner Firewall, the tunnel never completes IKEv1 Phase 1 and stays in MM_WAIT_MSG_6. Reachability between firewalls over internet is verified, ISAKMP UDP-500 is permitted end-to-end, and the IKE phase1 policy parameters including encryption, hashing, DH Group and lifetime matches exactly on both ends. Which configuration action must be done to resolve the issue?
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.
Which Cisco IOS XE command rejects packets with a source IP address that fails a reverse path forwarding prefix check on the ingress interface?
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.
Which security principle advocates rapid cryptographic algorithm replacement to defend against quantum-computing threats?
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.
A network engineer is configuring NTP authentication on a Cisco Catalyst Switch to ensure secure time synchronization. The engineer configures the client and NTP server by running the ntp authentication-key 10 md5 CiscoR45745212 command. The engineer must associate the NTP client at IP address 10.10.10.2 with the NTP server at IP address 10.10.10.1 using the correct key. Which configuration completes the requirement?
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.
A company wants to enforce security policy using Cisco Secure Access SIA. The design requirements are:
•Block adult content and gambling categories for all users
•Inspect file downloads for malware
•Bypass TLS decryption for financial and healthcare domains due to compliance
•Allow the marketing department to use social media, while keeping file scanning active for downloads from those sites.
Which two configuration actions must the engineer make on Cisco Secure Access SIG to meet the requirements? (Choose two.)
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.
Which protocol does the BYOD component in Cisco ISE use to obtain a unique device certificate from an internal CA?
Select an answer above, then submit your vote. Reading or practicing does not cast a vote.