logo
Exam overview and study plan

AZ-700 Practice Questions

Azure Network Engineer Associate

Read questions, check verified answers and discuss the reasoning. Use reading options to shape your revision, or switch to the simulator for timed practice.

View 164 free questions

164 questions in this view

Page 1 of 28

Question 1

Overview

Litware, Inc. is a financial company that has a main datacenter in Boston and 20 branch offices across the United States. Users have Android, iOS, and Windows 11 devices.

Existing Environment

Hybrid Environment

The on-premises network contains an Active Directory forest named litwareinc.com that syncs to a Microsoft Entra tenant named litwareinc.com by using Microsoft Entra Connect Sync.

All the offices connect to a virtual network named Vnet1 by using a Site-to-Site VPN connection.

Azure Environment

Litware has an Azure subscription named Sub1 that is linked to the litwareinc.com Microsoft Entra tenant. Sub1 contains resources in the East US Azure region as shown in the following table.

Name

Type

Description

Vnet1

Virtual network

Uses an IP address space of 192.168.0.0/20

GatewaySubnet

Virtual network subnet

Located in Vnet1 and uses an IP address space of 192.168.15.128/29

VPNGW1

VPN gateway

Deployed to Vnet1

Vnet2

Virtual network

Uses an IP address space of 192.168.16.0/20

SubnetA

Virtual network subnet

Located in Vnet2 and uses an IP address space of 192.168.16.0/24

Vnet3

Virtual network

Uses an IP address space of 192.168.32.0/20

cloud.litwareinc.com

Private DNS zone

None

VMScaleSet1

Virtual machine scale set

Contains four virtual machines deployed to SubnetA

VMScaleSet2

Virtual machine scale set

Contains two virtual machines deployed to SubnetA

storage1

Storage account

Has the public endpoint blocked

storage2

Storage account

Has the public endpoint blocked


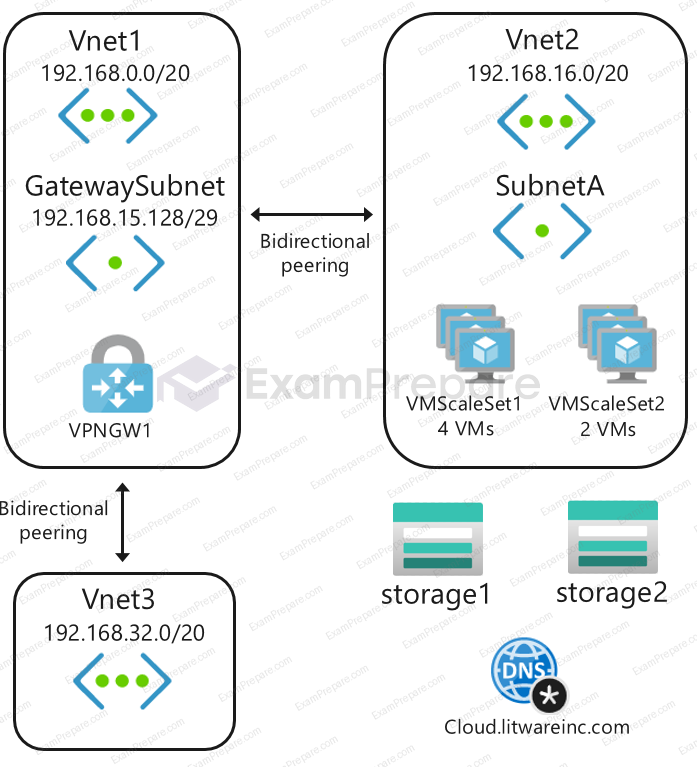
A diagram of the resources in the East US Azure region is shown in the Azure Network Diagram exhibit. (Click the Azure Network Diagram tab.) 

There is bidirectional peering between Vnet1 and Vnet2. There is bidirectional peering between Vnet1 and Vnet3. Currently, Vnet2 and Vnet3 cannot communicate directly.

Azure Network Diagram

Vnet1 uses an IP address space of 192.168.0.0/20. GatewaySubnet is in Vnet1 and uses an IP address space of 192.168.15.248/29. VPNGW1 is in to Vnet1.

SubnetA, VMScaleSet1 and VMScaleSet2 are in Vnet2. Bidirectional peering is configured between Vnet1 and Vnet2.

Vnet3 uses an IP address space of 192.168.32.0/20. Bidirectional peering is configured between Vnet1 and Vnet3.

storage1 and storage2 have public endpoints blocked.

Cloud.litwareinc.com is a private DNS zone

Requirements

Business Requirements

Litware wants to minimize costs whenever possible, as long as all other requirements are met.

Virtual Networking Requirements

Litware identifies the following virtual networking requirements:
  • Direct the default route of 0.0.0.0/0 on Vnet2 and Vnet3 to the Boston datacenter over an ExpressRoute circuit.
  • Ensure that the records in the cloud.litwareinc.com zone can be resolved from the on-premises locations.
  • Automatically register the DNS names of Azure virtual machines to the cloud.litwareinc.com zone.
  • Minimize the size of the subnets allocated to platform-managed services.
  • Allow traffic from VMScaleSet1 to VMScaleSet2 on the TCP port 443 only.

Hybrid Networking Requirements

Litware identifies the following hybrid networking requirements:
  • Users must be able to connect to Vnet1 by using a Point-to-Site (P2S) VPN when working remotely. Connections must be authenticated by Microsoft Entra ID.
  • Latency of the traffic between the Boston datacenter and all the virtual networks must be minimized.
  • The Boston datacenter must connect to the Azure virtual networks by using an ExpressRoute FastPath connection.
  • Traffic between Vnet2 and Vnet3 must be routed through Vnet1.

PaaS Networking Requirements

Litware identifies the following networking requirements for platform as a service (PaaS):
  • The storage1 account must be accessible from all on-premises locations without exposing the public endpoint of storage1.
  • The storage2 account must be accessible from Vnet2 and Vnet3 without exposing the public endpoint of storage2.
You need to prepare Vnet1 for the deployment of an ExpressRoute gateway. The solution must meet the hybrid connectivity requirements and the business requirements.

Which three actions should you perform in sequence for Vnet1? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

Actions

Answer Area

    Question 2

    Overview

    Litware, Inc. is a financial company that has a main datacenter in Boston and 20 branch offices across the United States. Users have Android, iOS, and Windows 11 devices.

    Existing Environment

    Hybrid Environment

    The on-premises network contains an Active Directory forest named litwareinc.com that syncs to a Microsoft Entra tenant named litwareinc.com by using Microsoft Entra Connect Sync.

    All the offices connect to a virtual network named Vnet1 by using a Site-to-Site VPN connection.

    Azure Environment

    Litware has an Azure subscription named Sub1 that is linked to the litwareinc.com Microsoft Entra tenant. Sub1 contains resources in the East US Azure region as shown in the following table.

    Name

    Type

    Description

    Vnet1

    Virtual network

    Uses an IP address space of 192.168.0.0/20

    GatewaySubnet

    Virtual network subnet

    Located in Vnet1 and uses an IP address space of 192.168.15.128/29

    VPNGW1

    VPN gateway

    Deployed to Vnet1

    Vnet2

    Virtual network

    Uses an IP address space of 192.168.16.0/20

    SubnetA

    Virtual network subnet

    Located in Vnet2 and uses an IP address space of 192.168.16.0/24

    Vnet3

    Virtual network

    Uses an IP address space of 192.168.32.0/20

    cloud.litwareinc.com

    Private DNS zone

    None

    VMScaleSet1

    Virtual machine scale set

    Contains four virtual machines deployed to SubnetA

    VMScaleSet2

    Virtual machine scale set

    Contains two virtual machines deployed to SubnetA

    storage1

    Storage account

    Has the public endpoint blocked

    storage2

    Storage account

    Has the public endpoint blocked


    A diagram of the resources in the East US Azure region is shown in the Azure Network Diagram exhibit. (Click the Azure Network Diagram tab.) 

    There is bidirectional peering between Vnet1 and Vnet2. There is bidirectional peering between Vnet1 and Vnet3. Currently, Vnet2 and Vnet3 cannot communicate directly.

    Azure Network Diagram

    Vnet1 uses an IP address space of 192.168.0.0/20. GatewaySubnet is in Vnet1 and uses an IP address space of 192.168.15.248/29. VPNGW1 is in to Vnet1.

SubnetA, VMScaleSet1 and VMScaleSet2 are in Vnet2. Bidirectional peering is configured between Vnet1 and Vnet2.

Vnet3 uses an IP address space of 192.168.32.0/20. Bidirectional peering is configured between Vnet1 and Vnet3.

storage1 and storage2 have public endpoints blocked.

Cloud.litwareinc.com is a private DNS zone

    Requirements

    Business Requirements

    Litware wants to minimize costs whenever possible, as long as all other requirements are met.

    Virtual Networking Requirements

    Litware identifies the following virtual networking requirements:
    • Direct the default route of 0.0.0.0/0 on Vnet2 and Vnet3 to the Boston datacenter over an ExpressRoute circuit.
    • Ensure that the records in the cloud.litwareinc.com zone can be resolved from the on-premises locations.
    • Automatically register the DNS names of Azure virtual machines to the cloud.litwareinc.com zone.
    • Minimize the size of the subnets allocated to platform-managed services.
    • Allow traffic from VMScaleSet1 to VMScaleSet2 on the TCP port 443 only.

    Hybrid Networking Requirements

    Litware identifies the following hybrid networking requirements:
    • Users must be able to connect to Vnet1 by using a Point-to-Site (P2S) VPN when working remotely. Connections must be authenticated by Microsoft Entra ID.
    • Latency of the traffic between the Boston datacenter and all the virtual networks must be minimized.
    • The Boston datacenter must connect to the Azure virtual networks by using an ExpressRoute FastPath connection.
    • Traffic between Vnet2 and Vnet3 must be routed through Vnet1.

    PaaS Networking Requirements

    Litware identifies the following networking requirements for platform as a service (PaaS):
    • The storage1 account must be accessible from all on-premises locations without exposing the public endpoint of storage1.
    • The storage2 account must be accessible from Vnet2 and Vnet3 without exposing the public endpoint of storage2.
    You need to connect Vnet2 and Vnet3. The solution must meet the virtual networking requirements and the business requirements.

    Which two actions should you include in the solution? Each correct answer presents part of the solution.

    NOTE: Each correct selection is worth one point.

    Select an answer above, then submit your vote. Reading or practicing does not cast a vote.

    Question 3

    Overview

    Litware, Inc. is a financial company that has a main datacenter in Boston and 20 branch offices across the United States. Users have Android, iOS, and Windows 11 devices.

    Existing Environment

    Hybrid Environment

    The on-premises network contains an Active Directory forest named litwareinc.com that syncs to a Microsoft Entra tenant named litwareinc.com by using Microsoft Entra Connect Sync.

    All the offices connect to a virtual network named Vnet1 by using a Site-to-Site VPN connection.

    Azure Environment

    Litware has an Azure subscription named Sub1 that is linked to the litwareinc.com Microsoft Entra tenant. Sub1 contains resources in the East US Azure region as shown in the following table.

    Name

    Type

    Description

    Vnet1

    Virtual network

    Uses an IP address space of 192.168.0.0/20

    GatewaySubnet

    Virtual network subnet

    Located in Vnet1 and uses an IP address space of 192.168.15.128/29

    VPNGW1

    VPN gateway

    Deployed to Vnet1

    Vnet2

    Virtual network

    Uses an IP address space of 192.168.16.0/20

    SubnetA

    Virtual network subnet

    Located in Vnet2 and uses an IP address space of 192.168.16.0/24

    Vnet3

    Virtual network

    Uses an IP address space of 192.168.32.0/20

    cloud.litwareinc.com

    Private DNS zone

    None

    VMScaleSet1

    Virtual machine scale set

    Contains four virtual machines deployed to SubnetA

    VMScaleSet2

    Virtual machine scale set

    Contains two virtual machines deployed to SubnetA

    storage1

    Storage account

    Has the public endpoint blocked

    storage2

    Storage account

    Has the public endpoint blocked


    A diagram of the resources in the East US Azure region is shown in the Azure Network Diagram exhibit. (Click the Azure Network Diagram tab.) 

    There is bidirectional peering between Vnet1 and Vnet2. There is bidirectional peering between Vnet1 and Vnet3. Currently, Vnet2 and Vnet3 cannot communicate directly.

    Azure Network Diagram

    Vnet1 uses an IP address space of 192.168.0.0/20. GatewaySubnet is in Vnet1 and uses an IP address space of 192.168.15.248/29. VPNGW1 is in to Vnet1.

SubnetA, VMScaleSet1 and VMScaleSet2 are in Vnet2. Bidirectional peering is configured between Vnet1 and Vnet2.

Vnet3 uses an IP address space of 192.168.32.0/20. Bidirectional peering is configured between Vnet1 and Vnet3.

storage1 and storage2 have public endpoints blocked.

Cloud.litwareinc.com is a private DNS zone

    Requirements

    Business Requirements

    Litware wants to minimize costs whenever possible, as long as all other requirements are met.

    Virtual Networking Requirements

    Litware identifies the following virtual networking requirements:
    • Direct the default route of 0.0.0.0/0 on Vnet2 and Vnet3 to the Boston datacenter over an ExpressRoute circuit.
    • Ensure that the records in the cloud.litwareinc.com zone can be resolved from the on-premises locations.
    • Automatically register the DNS names of Azure virtual machines to the cloud.litwareinc.com zone.
    • Minimize the size of the subnets allocated to platform-managed services.
    • Allow traffic from VMScaleSet1 to VMScaleSet2 on the TCP port 443 only.

    Hybrid Networking Requirements

    Litware identifies the following hybrid networking requirements:
    • Users must be able to connect to Vnet1 by using a Point-to-Site (P2S) VPN when working remotely. Connections must be authenticated by Microsoft Entra ID.
    • Latency of the traffic between the Boston datacenter and all the virtual networks must be minimized.
    • The Boston datacenter must connect to the Azure virtual networks by using an ExpressRoute FastPath connection.
    • Traffic between Vnet2 and Vnet3 must be routed through Vnet1.

    PaaS Networking Requirements

    Litware identifies the following networking requirements for platform as a service (PaaS):
    • The storage1 account must be accessible from all on-premises locations without exposing the public endpoint of storage1.
    • The storage2 account must be accessible from Vnet2 and Vnet3 without exposing the public endpoint of storage2.
    You need to recommend a configuration for the ExpressRoute connection from the Boston datacenter. The solution must meet the hybrid networking requirements and the business requirements.

    What should you recommend? To answer, select the appropriate options in the answer area.

    NOTE: Each correct selection is worth one point.
    Set the ExpressRoute gateway type to:
    To minimize latency of traffic to Vnet2:

    Question 4

    Overview

    Litware, Inc. is a financial company that has a main datacenter in Boston and 20 branch offices across the United States. Users have Android, iOS, and Windows 11 devices.

    Existing Environment

    Hybrid Environment

    The on-premises network contains an Active Directory forest named litwareinc.com that syncs to a Microsoft Entra tenant named litwareinc.com by using Microsoft Entra Connect Sync.

    All the offices connect to a virtual network named Vnet1 by using a Site-to-Site VPN connection.

    Azure Environment

    Litware has an Azure subscription named Sub1 that is linked to the litwareinc.com Microsoft Entra tenant. Sub1 contains resources in the East US Azure region as shown in the following table.

    Name

    Type

    Description

    Vnet1

    Virtual network

    Uses an IP address space of 192.168.0.0/20

    GatewaySubnet

    Virtual network subnet

    Located in Vnet1 and uses an IP address space of 192.168.15.128/29

    VPNGW1

    VPN gateway

    Deployed to Vnet1

    Vnet2

    Virtual network

    Uses an IP address space of 192.168.16.0/20

    SubnetA

    Virtual network subnet

    Located in Vnet2 and uses an IP address space of 192.168.16.0/24

    Vnet3

    Virtual network

    Uses an IP address space of 192.168.32.0/20

    cloud.litwareinc.com

    Private DNS zone

    None

    VMScaleSet1

    Virtual machine scale set

    Contains four virtual machines deployed to SubnetA

    VMScaleSet2

    Virtual machine scale set

    Contains two virtual machines deployed to SubnetA

    storage1

    Storage account

    Has the public endpoint blocked

    storage2

    Storage account

    Has the public endpoint blocked


    A diagram of the resources in the East US Azure region is shown in the Azure Network Diagram exhibit. (Click the Azure Network Diagram tab.) 

    There is bidirectional peering between Vnet1 and Vnet2. There is bidirectional peering between Vnet1 and Vnet3. Currently, Vnet2 and Vnet3 cannot communicate directly.

    Azure Network Diagram

    Vnet1 uses an IP address space of 192.168.0.0/20. GatewaySubnet is in Vnet1 and uses an IP address space of 192.168.15.248/29. VPNGW1 is in to Vnet1.

SubnetA, VMScaleSet1 and VMScaleSet2 are in Vnet2. Bidirectional peering is configured between Vnet1 and Vnet2.

Vnet3 uses an IP address space of 192.168.32.0/20. Bidirectional peering is configured between Vnet1 and Vnet3.

storage1 and storage2 have public endpoints blocked.

Cloud.litwareinc.com is a private DNS zone

    Requirements

    Business Requirements

    Litware wants to minimize costs whenever possible, as long as all other requirements are met.

    Virtual Networking Requirements

    Litware identifies the following virtual networking requirements:
    • Direct the default route of 0.0.0.0/0 on Vnet2 and Vnet3 to the Boston datacenter over an ExpressRoute circuit.
    • Ensure that the records in the cloud.litwareinc.com zone can be resolved from the on-premises locations.
    • Automatically register the DNS names of Azure virtual machines to the cloud.litwareinc.com zone.
    • Minimize the size of the subnets allocated to platform-managed services.
    • Allow traffic from VMScaleSet1 to VMScaleSet2 on the TCP port 443 only.

    Hybrid Networking Requirements

    Litware identifies the following hybrid networking requirements:
    • Users must be able to connect to Vnet1 by using a Point-to-Site (P2S) VPN when working remotely. Connections must be authenticated by Microsoft Entra ID.
    • Latency of the traffic between the Boston datacenter and all the virtual networks must be minimized.
    • The Boston datacenter must connect to the Azure virtual networks by using an ExpressRoute FastPath connection.
    • Traffic between Vnet2 and Vnet3 must be routed through Vnet1.

    PaaS Networking Requirements

    Litware identifies the following networking requirements for platform as a service (PaaS):
    • The storage1 account must be accessible from all on-premises locations without exposing the public endpoint of storage1.
    • The storage2 account must be accessible from Vnet2 and Vnet3 without exposing the public endpoint of storage2.
    You need to provide connectivity to storage1. The solution must meet the PaaS networking requirements and the business requirements.

    What should you include in the solution?

    Select an answer above, then submit your vote. Reading or practicing does not cast a vote.

    Question 5

    Overview

    Litware, Inc. is a financial company that has a main datacenter in Boston and 20 branch offices across the United States. Users have Android, iOS, and Windows 11 devices.

    Existing Environment

    Hybrid Environment

    The on-premises network contains an Active Directory forest named litwareinc.com that syncs to a Microsoft Entra tenant named litwareinc.com by using Microsoft Entra Connect Sync.

    All the offices connect to a virtual network named Vnet1 by using a Site-to-Site VPN connection.

    Azure Environment

    Litware has an Azure subscription named Sub1 that is linked to the litwareinc.com Microsoft Entra tenant. Sub1 contains resources in the East US Azure region as shown in the following table.

    Name

    Type

    Description

    Vnet1

    Virtual network

    Uses an IP address space of 192.168.0.0/20

    GatewaySubnet

    Virtual network subnet

    Located in Vnet1 and uses an IP address space of 192.168.15.128/29

    VPNGW1

    VPN gateway

    Deployed to Vnet1

    Vnet2

    Virtual network

    Uses an IP address space of 192.168.16.0/20

    SubnetA

    Virtual network subnet

    Located in Vnet2 and uses an IP address space of 192.168.16.0/24

    Vnet3

    Virtual network

    Uses an IP address space of 192.168.32.0/20

    cloud.litwareinc.com

    Private DNS zone

    None

    VMScaleSet1

    Virtual machine scale set

    Contains four virtual machines deployed to SubnetA

    VMScaleSet2

    Virtual machine scale set

    Contains two virtual machines deployed to SubnetA

    storage1

    Storage account

    Has the public endpoint blocked

    storage2

    Storage account

    Has the public endpoint blocked


    A diagram of the resources in the East US Azure region is shown in the Azure Network Diagram exhibit. (Click the Azure Network Diagram tab.) 

    There is bidirectional peering between Vnet1 and Vnet2. There is bidirectional peering between Vnet1 and Vnet3. Currently, Vnet2 and Vnet3 cannot communicate directly.

    Azure Network Diagram

    Vnet1 uses an IP address space of 192.168.0.0/20. GatewaySubnet is in Vnet1 and uses an IP address space of 192.168.15.248/29. VPNGW1 is in to Vnet1.

SubnetA, VMScaleSet1 and VMScaleSet2 are in Vnet2. Bidirectional peering is configured between Vnet1 and Vnet2.

Vnet3 uses an IP address space of 192.168.32.0/20. Bidirectional peering is configured between Vnet1 and Vnet3.

storage1 and storage2 have public endpoints blocked.

Cloud.litwareinc.com is a private DNS zone

    Requirements

    Business Requirements

    Litware wants to minimize costs whenever possible, as long as all other requirements are met.

    Virtual Networking Requirements

    Litware identifies the following virtual networking requirements:
    • Direct the default route of 0.0.0.0/0 on Vnet2 and Vnet3 to the Boston datacenter over an ExpressRoute circuit.
    • Ensure that the records in the cloud.litwareinc.com zone can be resolved from the on-premises locations.
    • Automatically register the DNS names of Azure virtual machines to the cloud.litwareinc.com zone.
    • Minimize the size of the subnets allocated to platform-managed services.
    • Allow traffic from VMScaleSet1 to VMScaleSet2 on the TCP port 443 only.

    Hybrid Networking Requirements

    Litware identifies the following hybrid networking requirements:
    • Users must be able to connect to Vnet1 by using a Point-to-Site (P2S) VPN when working remotely. Connections must be authenticated by Microsoft Entra ID.
    • Latency of the traffic between the Boston datacenter and all the virtual networks must be minimized.
    • The Boston datacenter must connect to the Azure virtual networks by using an ExpressRoute FastPath connection.
    • Traffic between Vnet2 and Vnet3 must be routed through Vnet1.

    PaaS Networking Requirements

    Litware identifies the following networking requirements for platform as a service (PaaS):
    • The storage1 account must be accessible from all on-premises locations without exposing the public endpoint of storage1.
    • The storage2 account must be accessible from Vnet2 and Vnet3 without exposing the public endpoint of storage2.
    You need to restrict traffic from VMScaleSet1 to VMScaleSet2. The solution must meet the virtual networking requirements.

    What is the minimum number of custom NSG rules and NSG assignments required? To answer, select the appropriate options in the answer area.

    NOTE: Each correct selection is worth one point.

    Question 6

    Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.


    After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.


    You have an Azure subscription that contains an Azure Front Door Premium profile named AFD1 and an Azure Web Application Firewall (WAF) policy named WAF1. AFD1 is associated with WAF1.


    You need to configure a rate limit for incoming requests to AFD1.

    Solution: You configure a custom rule for WAF1.


    Does this meet the goal?

    Select an answer above, then submit your vote. Reading or practicing does not cast a vote.